
WordPress Backdoor là gì?
Hàng nghìn site WordPress bị nhiễm mỗi năm và con số tăng. Chủ site/dev thường bỏ qua infection. Infection có thể persistent (dài hạn) hoặc không. WordPress Backdoor giúp duy trì sự bền bỉ này. Backdoor WP là code cho phép attacker unauthorized persistent access vào server. Thường là file độc ẩn ở đâu đó. Hoặc plugin bị nhiễm. Biến thể backdoor mới xuất hiện hàng tháng.
Hacker luôn cố gắng tiêm WP Backdoor. Nhiều plugin qua các năm dùng để lan truyền infection. Nguy cơ từ đâu cũng có thể đến. Sau này, xóa WP Backdoor là quá trình lâu & tốn resource. Tuy nhiên biện pháp phòng trừ luôn kiểm soát thiệt hại. Site WP secure có thể delay hoặc prevent attack. Xem chi tiết finding & fixing WP Backdoor.
Related Guide – Complete WordPress Security Guide (Reduce Hack Risk 90%)
Nguyên nhân dẫn đến WP Backdoor Hack
Setup WP dễ dàng. Nhưng nhiều lỗ hổng mở đường cho backdoor. Rút gọn top causes:
- Plugin buggy hoặc theme.
- Login credential yếu/mặc định.
- File permission yếu → expose file nhạy cảm.
- Không dùng WAF/Firewall/security solution.
- Cài đặt cũ (outdated).
- Chia sẻ server nhiễm với site khác. Yêu cầu provider cấp subnet.
Tìm WordPress Backdoor
Backdoor trong Theme
Theme inactive = nơi lý tưởng ẩn backdoor. Hacker biết & tìm theme inactive. Bạn ít check vì inactive. WP Theme có file critical functions.php – gọi PHP native, WP functions & khác. Có thể dùng để thực thi bất kỳ operation nào. Attacker thường inject file này để lấy backdoor. Ví dụ:
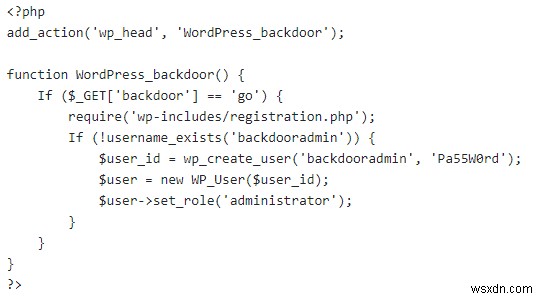
Code độc trong functions.php. Trigger khi attacker truy cập URL: www.yoursite.com/wp-includes/registration.php. Function tạo user mới:
id: backdooradmin
password: Pa55W0rd.
Dù bạn xóa user, attacker truy cập URL → tạo lại. Typical WP Backdoor example. Nhưng code này chỉ inject được sau khi đã có server access (open FTP port hoặc lỗ hổng khác).
Backdoor trong Plugin
WP Backdoor hack thường do plugin buggy. Plugin Contact Form 7 (5M+ active user) vừa bị bug privilege escalation. File plugin sửa đổi có thể không hiện trên dashboard. FTP search reveal. Backdoor file thường đặt tên "helper file" để trông legit. Lý do backdoor ở plugin:
- Plugin unused dễ bị infect – ẩn backdoor lâu.
- Plugin untrusted/unpopular thường code kém → tăng hack chance.
- Plugin outdated dễ bị target – nhiều người chạy không update.
- Plugin buggy giúp sửa file core khác.
→ Quét tất cả plugin lạ. Dọn plugin unused!
Backdoor trong Core Installation Files
Sửa core file sau khi plugin nhiễm. Có thể có code trái phép trong core file hoặc file mới xuất hiện. Backdoor đôi khi trông như gibberish:
$t43="l/T6\\:aAcNLn#?rP}1\rG_ -s`SZ\$58t\n7E{.*]ixy3h,COKR2dW[0!U\tuQIHf4bYm>wFz<admin@wsxdn.com&(BjX'~|ge%p+oMJv^);\"k9";
$GLOBALS['ofmhl60'] = ${$t43[20].$t43...
Code obfuscated bằng kỹ thuật known – khó đọc. Watch out code "fishy" & xóa file chứa nó. Backdoor cũng giả vờ file legit: xml.php, media.php, plugin.php… → đừng bỏ qua file nào dù trông legit. Các kỹ thuật khác làm code khó đọc.
Cũng tìm từ khóa FilesMan trong file. Ví dụ dump Filesman: 02 – backdoor nổi tiếng khó detect, không hiện log. Dùng steal password & detail.
<?php
$auth_pass = "";
$color = "#df5";
$default_action = "FilesMan";
$default_charset = "Windows-1251";
preg_replace("/.*/e","x65x76x61x6Cx28x67x7Ax69x6Ex66x6Cx61x74x65x28x62x61x73x65x36x34x5Fx64x65x63x6Fx64x65x28'7b1tVxs50jD8OXvO9R9Er3fanhhjm2Q2Y7ADIZCQSSAD5GUC3N623bZ7aLs93W0Mk+W/31Wll5b6xZhkdq/7OedhJtDdKpVKUkkqlapK3rDM1tzJLL4tl7qn+ycf90/O7ddnZ++7H+Ctu/t..NRCty4s8Uh1VQKxLg+xQC0T93+IV4sxw/c08okR1wKtoyadLX6Dl6tDg3WxVxFoHhkj6Yn/xc='x29x29x29x3B",".");
?>
Dòng 6: hex format. Convert → preg_replace("/.*/e","eval(gzinfla\. Dùng online tool decode hex. Attacker cũng dùng base64 obfuscation – xử lý tương tự. Từ khóa FilesMan ở dòng 4 – variant infection có keyword này. Code có thể alter file nhạy cảm như .htaccess – check kỹ!
Cách fix WordPress Backdoor Hack
Checksum Comparison
Bước 1: So sánh checksum. Heuristic xác định file integrity. Manual inspection hoặc free auto tool. Không chỉ core file, checksum cũng có cho plugin/theme. Maintain personal blacklist từ public list. Khi checksum mismatch → manual remove backdoor.
Core File Integrity
Bước 2: Sau khi file checksum khác, inspect manual. Backdoor hack chắc chắn alter file. Verify core file integrity. Download WP fresh copy.
$ mkdir WordPress
$ cd WordPress
$ wget https://github.com/WordPress/WordPress/archive/4.9.8.zip
$ tar -zxvf 4.9.8.zip
Tạo dir WP, switch vào, download latest (4.9.8), extract. Bước critical: $ diff -r path/to/your/file.php /Wordpress/wp-cron.php – so sánh 2 file. Backdoor đã sửa file → show diff. File dynamic như xmlrpc.php (RPC interaction) – hacker biết & ẩn backdoor ở đây. Check kỹ!
Encodings (Base64, Hex…)
File sửa đổi nhưng unreadable. Clean backdoor hack bằng tìm encoding base64. grep command powerful. Chạy:
find . -name "*.php" -exec grep "base64"'{}'\; -print &> output.txtLiệt kê detection base64 vào output.txt. Decode bằng online tools. Muốn search file khác .php → thay *.php. Malware cũng có hex format: grep -Pr "[\x01\x02\x03]". Lặp cho encoding khác. Xóa file/dòng code độc.
Server Logs
Server log giúp remove backdoor. Xem file modified sau date cụ thể. Check FTP log: IP nào connect server. Theo dõi file recently modified. Check image folder – không ai ngờ executable trong image folder. Image folder thường writable → hacker love hide there. Đảm bảo permission đúng cho file nhạy cảm: 444 (r--r--r--) hoặc 440 (r--r----). Check kỹ image folder modification.
Update & Backup
Tầm quan trọng update WP nhấn mạnh nhiều lần. Install cũ = install nhiễm.
Không trace được nguyên nhân backdoor hack → restore từ backup, CHỈ SAU KHI backup site hiện tại, rồi compare 2 bản.
Không backup sạch & muốn replace core file bằng mới: update WP manually sau khi backup site hiện tại.
Vuln report với plugin bạn dùng → update ngay. Patch lâu → replace alternative. Theo dõi blog official để có patch sớm nhất.
Dùng WordPress Backdoor Scanner
Con người hay sai sót. Manual inspection mệt & error-prone → miss backdoor. Giải pháp: Automation. Tool advanced hiện nay detect & remove WP Backdoor. Ví dụ: Astra Malware Cleaner. Không chỉ clean site, còn protect future infection. Giá hợp lý, full visibility. Tiết kiệm resource & time quý!