
Magento chạy 1,2% Internet và 12% tất cả site e-commerce. Số liệu: 250.000 site active dùng Magento.
Vì xử lý lượng lớn dữ liệu khách hàng, Magento thành mục tiêu #1 của hacker. Chúng tôi xây dựng quy trình xóa hack Magento từng bước. Hướng dẫn bao gồm triệu chứng, ví dụ, nguyên nhân, phòng trừ.
Dù nhiều loại hack Magento, Credit Card Skimming & Identity Theft phổ biến nhất. CVE details Magento tiết lộ vector tấn công nguy hiểm nhất:
[Chart by Visualizer]
Ngoài ra, vuln nghiêm trọng khiến Magento phải phát hành SUPEE-10266. Tấn công 'Magento Killer' mới diễn ra vài tháng trước. Support chính thức Magento 1 sắp kết thúc – store chưa mitigate sẽ mời hacker.
Magento Hacked: Triệu chứng & Hậu quả
Triệu chứng
- Khách khiếu nại thẻ tín dụng bị đánh cắp.
- Trang checkout có form giả thêm, mất doanh thu.
- Search engine blacklist store.
- Host suspend website.
- Redirect độc hại xuất hiện.
- Admin panel trắng / blank screen sau login.
- Store chậm, báo lỗi.
- Admin mồi (rogue admin) xuất hiện trong DB login.
- Google hiển thị kết quả spam keyword (tiếng Nhật / dược phẩm) cho site bạn.
Hậu quả
- Giảm traffic & doanh thu.
- Ảnh hưởng xấu SEO.
- Khách mất niềm tin, không truy cập.
- Dữ liệu site bị bán trên dark web cho đối thủ.
- Đánh cắp dữ liệu nhạy cảm qua phishing/JS.
Cần hỗ trợ chuyên nghiệp xóa hack Magento? Follow link này.
Ví dụ Magento Hack
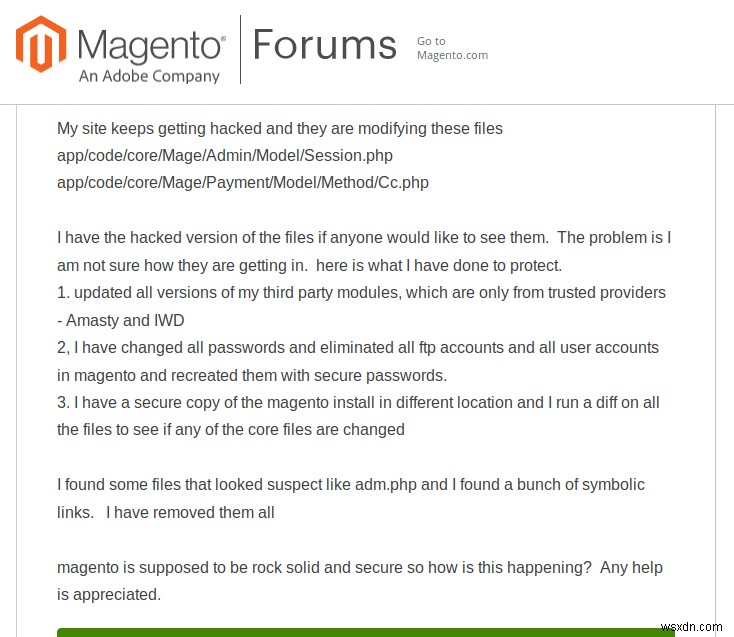
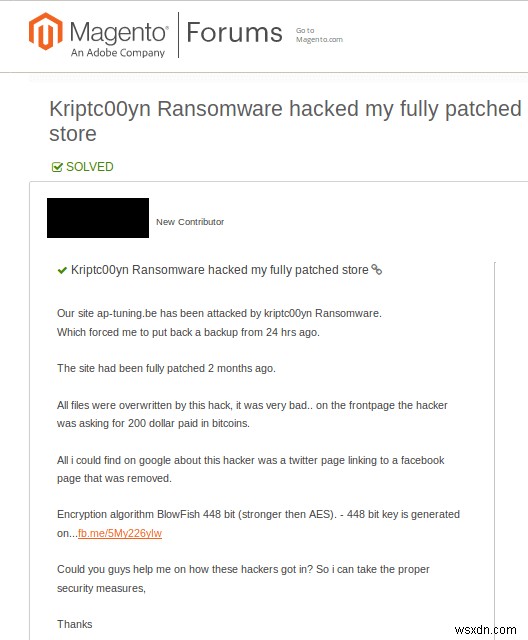
Nhiều admin không phải expert security →求助 community forum. Screenshot minh họa:
Magento site bị hack? Nhắn tin chat widget – Astra hỗ trợ. Hoặc sửa website ngay.
Nguyên nhân có thể của Magento Hack
Magento SQL Injection (SQLi)
SQLi phổ biến trên web app. Nhắm vào DB store – "bộ não" chứa dữ liệu nhạy cảm: lịch sử đơn hàng, transaction…
Tác động
- Attacker đọc nội dung DB.
- Sửa nội dung DB → sửa nội dung store.
- Xóa toàn bộ DB.
- Đánh cắp chi tiết thẻ tín dụng.
- Đánh cắp & lộ credential admin → mở đường tấn công tiếp.
- Reverse shell trong một số trường hợp → privilege escalation.
Ví dụ thực tế (Magento Shoplift 2015)
Target URL: https://www.example.com/index.php/admin/Cms_Wysiwyg/directive/index/
Nguyên nhân: parse error. Giá trị nhập vào key filter ("filter": malicious_value) bị parse sai. Attacker dùng base64 encoding bypass detection. Chèn SQL statement vào filter key → parsed & executed.
Decode request → SQL đầu set password mới với salt attacker chọn. Group sau insert admin_user mới vào DB. Group cuối leverage admin role. Kết quả: attacker tạo admin user = "ypwq", pass = "123". Exploit full public trên Github.
Phòng tránh SQLi
- Hạn chế privilege client-side.
- Dùng Prepared Statements.
- Bảo vệ tham số.
- Triển khai WAF/Firewall.
Magento XSS (Cross-Site Scripting)
Attacker inject JS độc vào các page store. Do yếu/kém sanitization & validation. Nhắm vào cookie & session detail. Mục đích: steal session user/admin → login unauthenticated.
Tác động
- Steal cookie/session.
- Unauthenticated access cho hacker.
- Đọc CSRF token & dữ liệu quan trọng.
- Gửi request giả mạo user.
Ví dụ: XSS Magento 1.9.0.1
File vulnerable:
https://[magento_url]/skin/adminhtml/default/default/media/editor.swf
https://[magento_url]/skin/adminhtml/default/default/media/uploader.swf
https://[magento_url]/skin/adminhtml/default/default/media/uploaderSingle.swf
Nguyên nhân: FlashVar parameter bridgeName truyền vào ExternalInterface.call без proper sanitization. Có thể inject JS độc qua bridgeName → execute mỗi lần load page. Full payload:
https://example.com/skin/adminhtml/default/default/media/editor.swf?bridgeName=1%22]%29%29;alert%281%29}catch%28e%29{alert%281%29}//Phòng tránh XSS
- Thiết lập rule sanitization & validation chuẩn.
- Hạn chế privilege.
Magento CSRF (Cross-Site Request Forgery)
CSRF thực thi request giả mạo thay mặt user cuối, không hay biết. Thường kèm social engineering: hacker gửi link độc đến target (thường admin) qua email. Mục đích: thực thi function thay mặt user.
Tác động
- Attacker xóa tài khoản bạn.
- Sử dụng thẻ tín dụng bạn.
- Chuyển tiền từ ngân hàng victim sang attacker.
- Đặt hàng bất hợp pháp trên store Magento (không thanh toán / thao túng giá).
Ví dụ
- CSRF bug nghiêm trọng Magento 1: attacker inject script code vào application-side module image upload. Vulnerable component: parameter filename của image upload module. Dùng POST request từ application-side. Cần low-privilege user account & low/medium user interaction. Code snippet vulnerable.
- Magento Community & Enterprise < 2.0.10/2.1.2: 2 CSRF bug.
- APPSEC-1212: Không validate anti-CSRF token khi xóa item từ mini-cart via GET request. Attacker xóa cart item qua phishing.
- APPSEC-1433: CSRF nghiêm trọng hơn. Attacker xóa bất kỳ địa chỉ nào trên store do thiếu anti-CSRF token / Referer header validation.
Phòng tránh CSRF
- Token-based prevention (best).
- Same-origin policy.
- Synchronizer tokens.
- Captcha.
Magento Remote Code Execution (RCE)
Cho phép attacker chèn code độc vào website.
Tác động
- Compromise website & web server.
- View, modify, delete file & DB.
Ví dụ: APPSEC-1484 (Critical 9.8)
Magento CE & EE < 2.0.10/2.1.2 vulnerable RCE. Nguyên nhân: payment method cho phép user execute PHP độc khi checkout. Exploit & Metasploit module public.
Phòng tránh RCE
- Thiết lập proper parsing methods.
- Strict user permissions.
Nguyên nhân khác
- Weak/hardcoded credentials.
- LFI, RFI, OWASP Top 10…
- Version cũ.
- Server misconfig (open ports…).
- Hosting kém, không subnet.
Dọn dẹp Magento Store bị hack
Damage Control (Kiểm soát thiệt hại)
Không fix hack nhưng dừng "cơn giận":
- Đổi credential mặc định/điển hình → mạnh, ngẫu nhiên, unique.
- Update user password bằng 1 câu SQL block tất cả attacker:
update users set pass = concat('ZZZ', sha(concat(pass, md5(rand())))); - Chặn truy cập folder nhạy cảm: tạo
.htaccessbên trong với:
Thay xx.xx.xx.xx = IP bạn. Thêm dòng Allow cho IP khác.Order Deny,Allow Deny from all Allow from xx.xx.xx.xx
Backup site
Trước khi clean, backup full: core files + DB. Include file tùy chỉnh (extension, theme). Backup: core, extensions, database.
Xác nhận hack
Dùng Tool
Quét store. Virustotal phổ biến nhất.
Google Search Console
- Login Google Search Console.
- Vào 'Security Issues' tab.
- Check flag. Site hack thường bị flag ngay. Xem báo cáo chi tiết: loại infection & file chính xác chứa malware.
Scan Core Files
Hacker inject code vào DB & core file. Check recent unknown modification.
SSH Command (diff với clean version)
Download Magento clean version từ official/Github. Command check anomaly:
$ mkdir magento-2.2.5
$ cd magento-2.2.5
$ wget https://github.com/magento/magento2/archive/2.2.5.tar.gz
$ tar -zxvf 2.2.5.tar.gz
$ diff -r 2.2.5 ./public_html
Note: Magento 2.2.5 làm clean file, public_html = current install.
Diff Command (file sửa đổi gần đây)
File recently modified luôn đáng ngờ. Diff reveal changes trong timeframe set (vd: mtime -15 = 15 ngày).
- SSH vào Magento server.
- Chạy:
$ find ./ -type f -mtime -10→ list changes 10 ngày qua. - SFTP: xem cột date modified cuối cùng.
Duyệt thủ công các thay đổi.
Audit User Logs
Kiểm tra user site. Hacker có thể add themselves as user. Audit admin table, xóa rogue user.
- Login admin panel.
- System > Permissions > All Users.
- Review kỹ list.
Hunt for Malware
SQLi: attacker hide code unreadable format. Base64 phổ biến. Tìm base64 trong file:
find . -name "*.php" -exec grep "base64"'{}'\; -print &> hiddencode.txtDecode bằng online tools để phân tích sâu.
Spam attack: gibberish inject mỗi page. Khó tìm/xóa. Dùng phpMyAdmin search malicious code nhiều page cùng lúc.
Magento Security: Restore Files
Sau khi lộ malware, xóa khỏi page hack. Code không chắc → comment out & contact experts. Restore từ backup. Không backup → dùng fresh copy.
Magento Hack Prevention
Update & Backup
Migrate sang Magento 2. Team Magento vá critical flaw mỗi update (check changelog). Tránh extension undeclared (chứa buggy code). Tạo site copy – hữu ích restore sau attack. Update & Backup = cách rẻ & hiệu quả nhất secure Magento store.
Complete Magento Security Guide (video, extension, code, infographic) – Giảm 90% rủi ro hack
Security Audit
Audit bảo vệ store. Không phải ai cũng expert security. Dùng service online như Astra. Astra Security Audit & Penetest khám phá threat nghiêm trọng. Vá vuln trước khi attacker exploit!
Astra: Magento Malware Scanner & Firewall Plugin
Vuln Magento mới mỗi tháng. Bảo vệ store khỏi fraud & malware chỉ $9/tháng. Astra cloud-deployed – không resource-heavy AV. User bình thường dùng thoải mái qua dashboard đơn giản. Cài Magento Firewall plugin dễ dàng, engineer Astra support nếu cần. Astra Firewall robust & scalable.
Magento Malware Scanner Astra detect & remove multiple malware signature từ hacked site trong vài phút. Cũng fix file cho bạn.
Thử Astra Demo ngay!