
Lịch sử, file văn bản thuần túy WindowsUpdate.log được dùng để phân tích hoạt động của Windows Update agent và service. Tuy nhiên, log Windows Update trong Windows 10 (Windows Server 2016/2019) được lưu ở định dạng Event Tracing for Windows (ETW), thay vì file text thông thường. Với hành động này, các nhà phát triển Windows dự định tăng hiệu suất hệ thống ghi log và giảm dung lượng file text trên ổ đĩa.
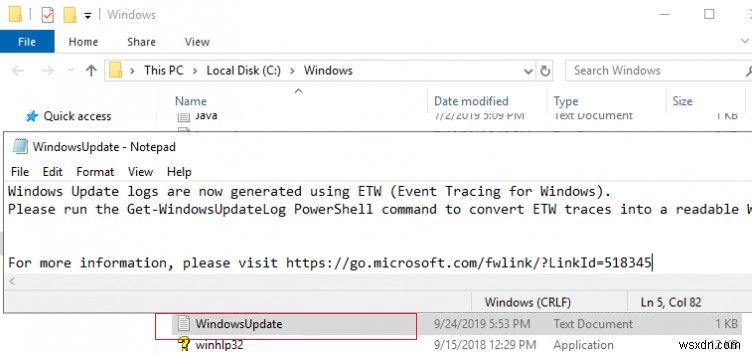
Do đó, các sự kiện Windows Update không còn được ghi real-time vào file %windir%\WindowsUpdate.log. Dù file vẫn hiện diện ở gốc thư mục Windows, nó chỉ nói rằng định dạng ETW hiện được dùng để thu thập log WU.
Windows Update logs are now generated using ETW (Event Tracing for Windows).Please run the Get-WindowsUpdateLog PowerShell command to convert ETW traces into a readable WindowsUpdate.log.
For more information, please visit https://go.microsoft.com/fwlink/?LinkId=518345
Nhược điểm của phương pháp ghi log mới cho admin – bây giờ bạn không thể nhanh chóng phân tích Windows Update Agent service, tìm mã lỗi trong file text WindowsUpdate.log (xem Danh sách hoàn chỉnh mã lỗi Windows Update), kiểm tra cài đặt WSUS agent và phân tích lịch sử cài đặt cập nhật.
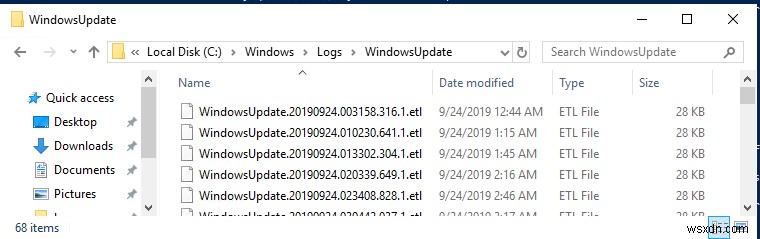
Bạn có thể chuyển đổi sự kiện ETW sang file text WindowsUpdate.log thuần túy để phân tích sự kiện dịch vụ cập nhật thuận tiện hơn. Để làm này, dùng cmdlet PowerShell – Get-WindowsUpdateLog. Cmdlet này cho phép thu thập thông tin từ tất cả file .etl (chúng lưu ở C:\WINDOWS\Logs\WindowsUpdate) và tạo một file text WindowsUpdate.log duy nhất.
Để tạo file WindowsUpdate.log và lưu ở C:\PS\Logs, chạy lệnh sau trong PowerShell console:
Get-WindowsUpdateLog -logpath C:\PS\Logs\WindowsUpdate.log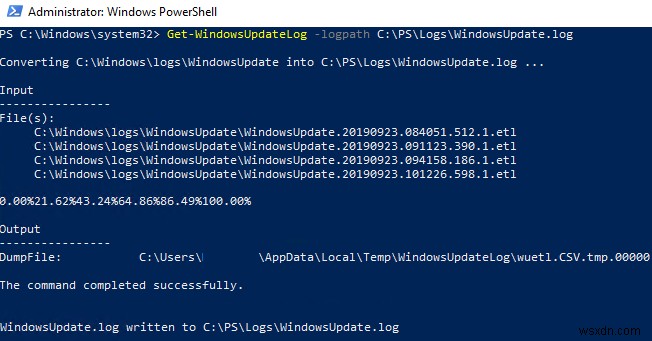
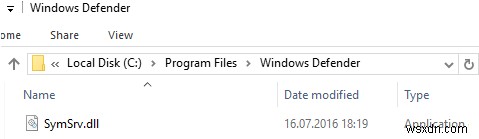
Trong Windows Server 2016, khi chạy cmdlet Get-WindowsUpdateLog, bạn có thể nhận lỗi "SymSrv.dll is missing":
Copy-Item : Cannot find path 'C:\Program Files\Windows Defender\SymSrv.dll' because it does not exist. At C:\Windows\system32\WindowsPowerShell\v1.0\Modules\WindowsUpdate\WindowsUpdateLog.psm1:56 char:5
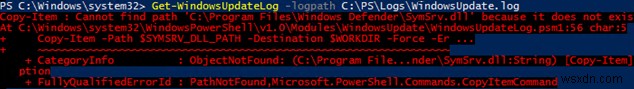
File "C:\Program Files\Windows Defender\SymSrv.dll" thường bị thiếu nếu Windows Defender không cài trên server.
Để sửa lỗi, bạn có thể cài Windows Defender, copy file SymSrv.dll từ Windows Server 2016/Windows 10 khác, hoặc tìm file SymSrv.dll trong thư mục WinSxS cục bộ (trong trường hợp tôi, thư mục gọi là C:\Windows\WinSxS\amd64_windows-defender-service-cloudclean_…) và copy vào thư mục "C:\Program Files\Windows Defender".
Trong các build Windows 10 cũ, lần đầu chạy cmdlet Get-WindowsUpdateLog, nó tải và cài Microsoft Internet Symbol Store. Phiên bản Windows 10 mới truy cập Microsoft Symbol Server trong Azure trực tuyến. Sau đó cmdlet:
- Đọc dữ liệu từ tất cả file .etl;
- Dữ liệu được chuyển đổi sang định dạng CSV (mặc định) hoặc XML;
- Dữ liệu từ file định dạng trung gian sẽ được chuyển đổi và thêm vào file log text chỉ định trong tham số LogPath (nếu tham số LogPath không chỉ định, WindowsUpdate.log được tạo trên desktop của user chạy lệnh)
Mẹo. Cách khác để phân tích file ETL, nhưng phức tạp hơn, là dùng tiện ích Tracefmt.exe để nhận dữ liệu từ .etl.
Mở file log bằng lệnh PowerShell này:
Invoke-Item -Path C:\PS\Logs\WindowsUpdate.log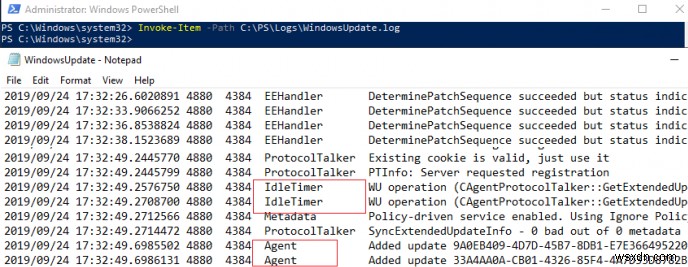
Trong một số trường hợp, trong file WindowsUpdate.log bạn có thể thấy chuỗi như:
Unknown(140): GUID=53212e4cc-4321-f43a-2123-9ada0090bc12b (No Format Information found).
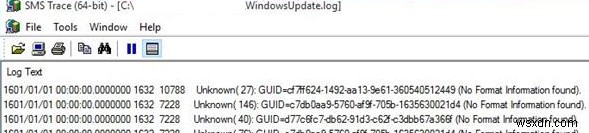
Điều này có nghĩa là bạn không cài Windows Symbol server (hôm nay bạn không thể tải bộ cài Windows symbols riêng biệt, vì nó tự động tải từ symbol store trong Azure). Đối với môi trường cách ly, bạn có thể dùng phiên bản offline của symbol server theo bài Offline Symbols for Windows Update.
Mẹo. Lưu ý file WindowsUpdate.log tạo ra là tĩnh (static) và không cập nhật real-time như phiên bản Windows trước. Để cập nhật file, bạn cần chạy lại cmdlet Get-WindowsUpdateLog hoặc tạo script tự động cập nhật file theo tần suất nào đó (file bị ghi đè).
Phân tích file WindowsUpdate.log kết quả khá khó vì nó thu thập dữ liệu từ nhiều nguồn sự kiện:
- AGENT – sự kiện Windows Update agent;
- AU – cập nhật tự động;
- AUCLNT – tương tác người dùng;
- HANDLER – quản lý trình cài đặt cập nhật;
- MISC – thông tin WU chung;
- PT – đồng bộ cập nhật với kho dữ liệu cục bộ;
- REPORT – thu thập báo cáo;
- SERVICE – sự kiện start/stop dịch vụ wuauserv;
- SETUP – cài đặt phiên bản mới Windows Update client;
- DownloadManager – tải cập nhật vào cache cục bộ dùng BITS;
- Handler, Setup – header trình cài đặt (CBS, v.v.);
- và nhiều khác.
Bạn có thể chọn 30 sự kiện cuối từ Windows Update Agent (agent) bằng biểu thức chính quy đơn giản:
Select-String -Pattern '\sagent\s' -Path C:\PS\Logs\WindowsUpdate.log | Select-Object -Last 30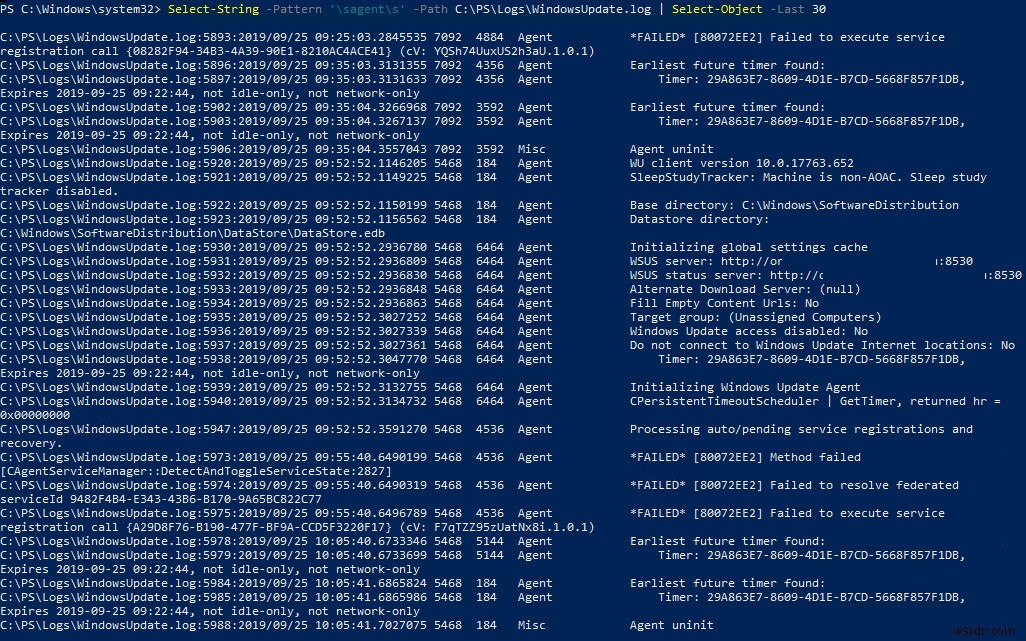
Bạn có thể lọc sự kiện trong WindowsUpdate.log theo nhiều nguồn:
Select-String -Pattern '\sagent\s|\smisc\s' -Path c:\PS\Logs\WindowsUpdate.log | Select-Object -Last 50Tương tự, bạn có thể parse file text cho sự kiện theo số KB, lỗi (FAILED, Exit Code, FATAL).
Bạn cũng có thể tạo file WindowsUpdate.log cho máy tính/server từ xa:
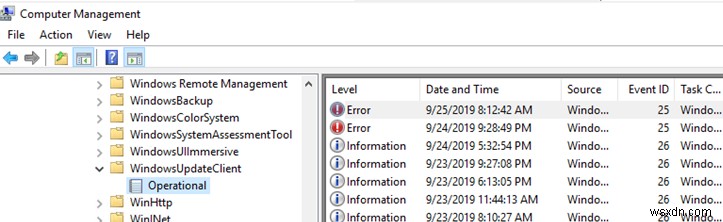
Get-WindowsUpdateLog -ETLPath \\ny-srf-1\C$\windows\Logs\WindowsUpdate -LogPath C:\PS\Logs\windowsupdate-ny-srf-1.logBạn cũng có thể dùng log Event Viewer để phân tích hoạt động dịch vụ Windows Update. Mở rộng mục Event View sau: Applications and Services Logs -> Microsoft -> Windows -> WindowsUpdateClient -> Operational.
Bạn có thể dùng module PSWindowsUpdate để quản lý cập nhật từ PowerShell cli.