
Đến đây, bạn fairly versed KVM. Đã có tutorials: basic intro, intermediate setup/use, network/storage configs, setup KVM alongside VirtualBox. Next logical step: bridged networking để VM có usable external IP addresses, forward ports...
Hôm nay show khác hầu hết tutorials elsewhere. Try work around brute-force approach. 2 methods expose VMs ra external world. 1 method là hack nhưng absolutely genius. Chưa bao giờ thấy! Talk limitations/problems.
Lưu ý: Ảnh từ Wikipedia, CC BY-SA 3.0; index teaser same terms.
Chuẩn Bị Cơ Bản
Reality check. Bridged networking hơi ugly, cần Linux command line understanding. Nhưng đôi khi bridging necessary. Chạy server trong VM -> muốn external IP, other hosts communicate directly.
VD: Router cấp range 10.0.0.X. Physical host 10.0.0.4, VM chạy 192.168.2.133. Không change system interpret packets -> clients 10.0.0 network không talk clients 192.168.2 network.
Workaround: bridging. Cho VM connect router, lease external IPs. "External" = whatever physical hosts dùng, không nhất thiết non-private.
Default KVM tạo bridge 192.168.122.1. Virtual router cho VMs, cấp IP range này. Nhưng muốn machines lease external addresses. Tutorial này: 192.168.2 range.
Hai giải pháp thay thế
Hai cách thử:
1) Tạo bridge. 2 devices bridged: physical eth1 và virtual vnet0. Ascertain bridge works -> commit changes network config file disk. VMs lease IP từ router. Giống VirtualBox. Method này cover here.
2) Không guaranteed work, nhưng just might. Nếu network adapter support bridging out of the box -> dùng trực tiếp. Chỉ change: assign small subnet addresses virtual bridge KVM, không overlap physical hosts network.
Limitations
Nhiều thứ wrong. Router không support bridging. Network interface không support bridging. IP lease pool limited. Firewall interfering. Cuối cùng, specific Ubuntu: Network Manager managing bridged interface -> problems/conflicts.
More reading: Bridge setup Linux Foundation, KVM Networking Ubuntu Community Documentation.
Bây giờ biết ahead. Bridging definitely not simple. Several things consider: 1) Network adapter support bridging? Laptop Wireless adapters không really support mode này. 2) Comfortable fiddle network settings? 3) Trying achieve gì? NAT good enough?
Basic Networking Concepts
Test box Ubuntu, nhưng tutorial distro-agnostic. Ubuntu KVM community docs good nhưng chỉ Debian-based. Deviate little, introduce networking concepts applicable RedHat/SUSE.
Debian-based (Ubuntu): persistent network configs /etc/network/interfaces. RedHat-based + SUSE: individual files /etc/sysconfig/network, prefix ifcfg-ethX hoặc ifcfg-eth-MAC-address. Replace generic eth với interface name thấy trên system (ifconfig).
Cũng tạo bridges brctl command line, không commit config files, settings lost restart network service. Recommended test first trước khi edit system files. Backup configs before fiddling. Details: Linux commands article.
Tạo Bridge
Ready to play. Suggest brctl, ifconfig, dhclient commands. Excuse không deep details. Popular demand -> extra tutorial. General sequence (sudo/root) - assume br0, physical/virtual eth0/1, DHCP lease switch/router:
ifconfig eth0 0.0.0.0
ifconfig eth1 0.0.0.0
brctl addbr br0
brctl addif br0 eth0
brctl addif br0 eth1
dhclient br0
Note: virtual adapter may not available until create/start VM. Cần không add virtual adapter yet. KVM tự động add nếu chọn bridged networking advanced options.
Nếu bridge interface lease external address DHCP server -> right track. Home users: DHCP server = router. Direct Internet connection: ISP không cho >1 IP/user.
Bridge lên -> ensure network functionality unchanged. May need edit /etc/resolv.conf, fix routing table.
Work -> commit changes network config file. Example generic, similar community docs. May need enable Spanning Tree Protocol (STP) bridge, handle multiple hops/cyclic routes.
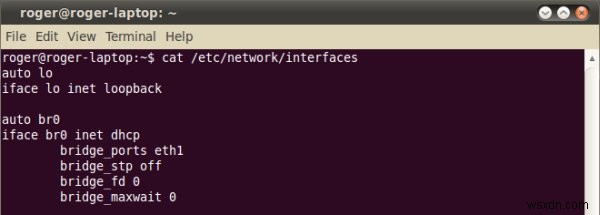
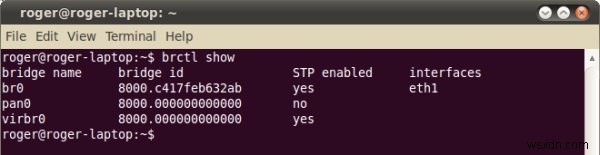
Specifically: edit /etc/network/interface add br0. Require STP: bridge_stp off -> bridge_stp on. Verify: brctl show.
STP fun - sounds naughty.
Tạo Virtual Machine
Learned previously, not new. Final stage, Advanced options: change network address assignment, ensure virtual adapter unique MAC address no conflict.
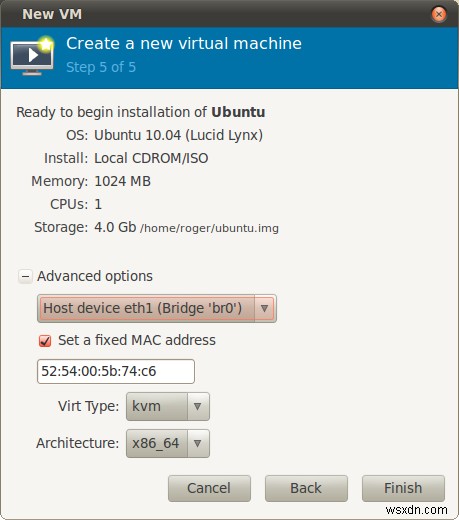
Lucky: không cần special bridging; network adapter support out of the box -> fine! But probably not lucky -> expect hard keyboard labor.
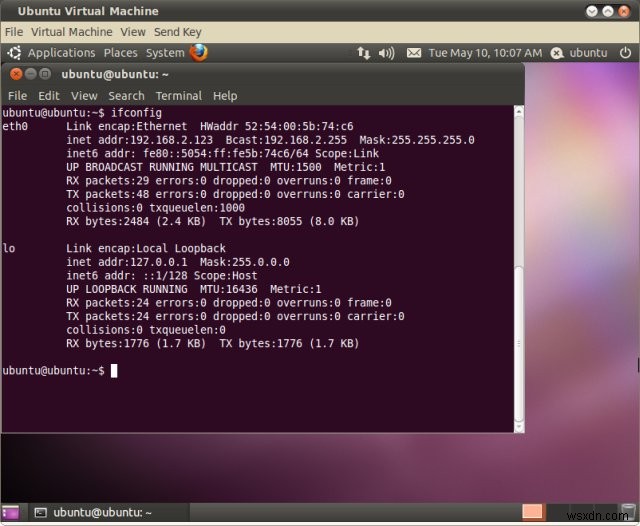
Make sure works:
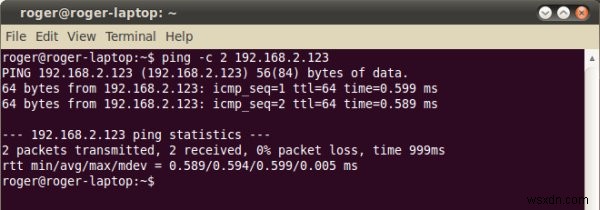
Ping it -> hack it. Gần giống VirtualBox. Expose services, share data, whatever. Enjoy.
Alternative Setup (Might Not Work, But Brilliant)
Không lucky. Network Manager refuse cooperate, ton other issues. Create separate virtual network adapter, route to physical device believed support bridging out of box. Mind conflicting IPs.
Finally, nếu work -> very dirty hack. Create virtual network share same /24 space network. VD: router 192.168.2.0 network, create virtual network start 192.168.2.160, small range 16 addresses. Ensure router never give those addresses other clients.
Example: network 192.168.2.160/28. Không expect router lease range đó, nhưng limit DHCP assignment. Route virtual network to physical device (Wireless adapter eth1).
Tạo VM route to eth1 như trên. Online -> lovely cooperation. Host .102, virtual NIC virbr1 .161, VM .168.
Ping từ physical Windows 7 box same network .103, ping virtual adapter .161 trên Ubuntu Lucid, both Wireless, same router -> cute/smart setup. Không luôn work, nhưng khi work -> genius.
Existing Virtual Machines
VMs existing: edit settings change directives /etc/libvirt/. Mỗi VM separate .xml config. Power cycle VMs cho effect. VD:
Kết Luận
KVM bridged networking setup không intuitive. Friendly như VirtualBox 2-3 năm trước. Manageable, nhưng real limitations: understanding và functionality network topology. Sẽ tốt hơn với thời gian.
Lucky: network adapters support bridging out of box. Không: tạo bridge adapter, assign physical/virtual devices. Resolve DNS/DHCP/routing issues. Finally dirty hack: abuse network ranges, subnet trong subnet, ensure IP không overlap, route virtual adapter to physical device.
Tutorial basic yet cunning twist, nhưng numerous issues left uncovered. Questions/suggestions/tips difficult KVM network setups -> mail me, might concoct sequel howto.
Cheers.