
Bạn từng muốn bỏ internet bill đắt đỏ dùng wifi neighbor insecure? Chỉ thing holding back là Honeybadger single-factor auth flow? Well, got news for you.
Announcing: Two Factor Authentication (2FA)
Joking aside, security rất serious. Thrilled provide important tool keep users và data secure.
Could explain how enable 2FA, but where's fun? Light-hearted glimpse into cryptography world figure out how 2FA works.
Fun not your thing, straight to How to enable, feelings not hurt.
⚠️ Warning: Some Theory Below
Nhiều 2FA implementations built trên algorithm Time-Based One-Time Password (TOTP). Rolls right off tongue.
One-Time?
Yes, beauty: không transmit same "password" mỗi lần login. Dùng authenticator app, one-time "password" generated valid short duration (보통 30 giây), greatly dilutes effectiveness man-in-the-middle attack.
Mặc dù complicated bits, overall implementation relatively simple.
The Secret
Key point understand TOTP: server (verifier) và authenticator (prover) phải có shared secret. Đây là real "password", nhưng chỉ transmitted once (so one-time cũng)!
Recommended way consume secret via QR code. Scan QR code vào smartphone, secret encoded trong standard URI như:
otpauth://totp/Honeybadger.io:inigo@honeybadger.io?secret=base32-secret-keyBenefits QR code (vs plaintext secret):
- Ai có time type 32-char code?
- Authenticator app cung cấp helpful labels cho one-time password (reference email và issuer trong URI). Useful khi 2FA multiple services.
- Finally good reason dùng QR code!
Additional (mostly ignored) parameters cho otpauth scheme, view here.
MAC And Me
Secrets agreed upon 🤝, asked (at some point) provide One-Time Password. Things get real.
TOTP built on top HMAC-Based One-Time Password (HOTP), based on Hash-based Message Authentication Code (HMAC). All one big crypto onion.
TOTP & HOTP basically variations on message gets hashed. HMAC where magic happens. HMAC produces digest, output running value through hashing algorithm. Ruby code:
OpenSSL::HMAC.digest("SHA1", "my-secret-key", "the-earth-is-flat")
=> "R\xABp\xCB\xEC\xFEJ\r#\x02\xC8\xAB\x96\xB68\v\xDA0\xD7z"
Wow, binary string! Đó là Message Authentication Code (MAC).
Chọn SHA1 hashing function (như TOTP implementation). Nhiều functions khác, each với security/performance implications. Radical về hashing algorithm: any input, same output every time! Cũng produce vastly different unique output từ subtle input changes (depends on function, but not terribly concerned collisions here).
Called Message Authentication Code vì dùng prove received message authentic. Nếu bạn và tôi know secret (my-secret-key), tôi send message the-earth-is-flat với MAC. Bạn run exact same digest function, same inputs, MACs match → authenticated message! Know not tampered và only từ tôi!
😎
Timecode
Bring back TOTP. Talk about time. Với TOTP, thay vì digest preposterous message như the-earth-is-flat, dùng time step count (converted to string) as input. Mở authenticator app, watch codes switch, notice pattern. Đúng, "They switch on the minute and the half minute", very good.
Calculating message simpler. Dùng rounded down count 30 seconds (time step) since beginning of time (unix time). Ruby:
Time.now.to_i / 30 => 51772900Ah hah! That's Message.
Authenticator app dùng digest function get new HMAC:
hmac = OpenSSL::HMAC.digest("SHA1", "avwe8aw71j2boib23jkbjk32", "51772900")
=> "H\x7F\xC1\xACL\xDA\xDB\xE7DQ\x91kE\x1C\xE3,c\nH\xA0"
get_otp_code(hmac) => "332204"
Last step: get number code từ binary string. Bit manipulation required, hide behind anonymous get_otp_code. Muốn đọc HOTP Spec.
Submit code to server, performs exact same digest operation compare codes. Match → in! Vì work với time, latency factor. Strategies account delays. Understanding = homework nếu muốn.
That's gist Time-Based One-Time Passwords!! 🎉 Feel free send thank you email sau dùng info life of next dinner party!
Implementation
Think important understand how things work, nhưng strongly discouraged roll-your-own anything crypto related. Great thing Ruby/Rails ecosystem: often find gem (sometimes many) solve problem.
Dùng devise at Honeybadger, great devise plugin two_factor_authentication. Few 2FA implementations choose from, reasons chose this:
- Simple setup (migration, config & initializers)
- Allow One-Time code entered own page (after valid user/password)
- Acceptable defaults, simple override
- Max login attempts check, recommended by spec
How To Enable
Setup simple: Navigate User Settings > Authentication, select "Set Up Two Factor Authentication", follow directions sync secret dùng Authy hoặc Google Authenticator (hoặc any TOTP app).
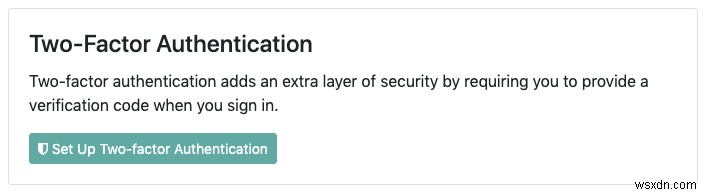
Xong! Next login, prompt authenticator code. Fill in và go với complete peace of mind. 🧘
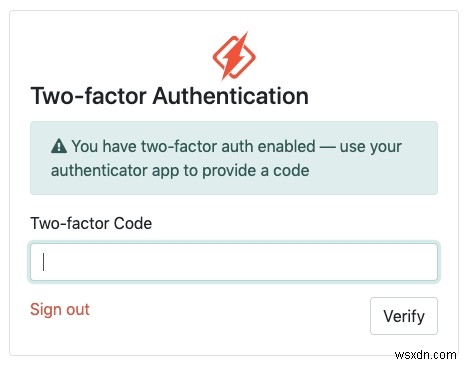
Security và simplicity? Better?
One Last Thing: Pwned Password Check
Quick one cho weak passwords proponents. Integrated với devise-pwned_password gem. Từ nay, operation yêu cầu password, check proposed password not prevalent known data breaches. Add new password fail check → not allow.
Nếu chưa, highly recommend password manager (1Password ahem).
Interesting bit Pwned Password: password stay secure even checking against 3rd party database. Called k-Anonymity, overview here.
That's all for now. Until next time! 👋